 JIJI LABS
 SHIPSAFE
Check your project before you ship.
SHIPSAFE scans a code project on your Mac for leaked API keys and risky release settings, and shows the file, the line and the evidence for each finding. It runs on your machine: no upload, no account.
Paid app · one-time purchase, no subscription
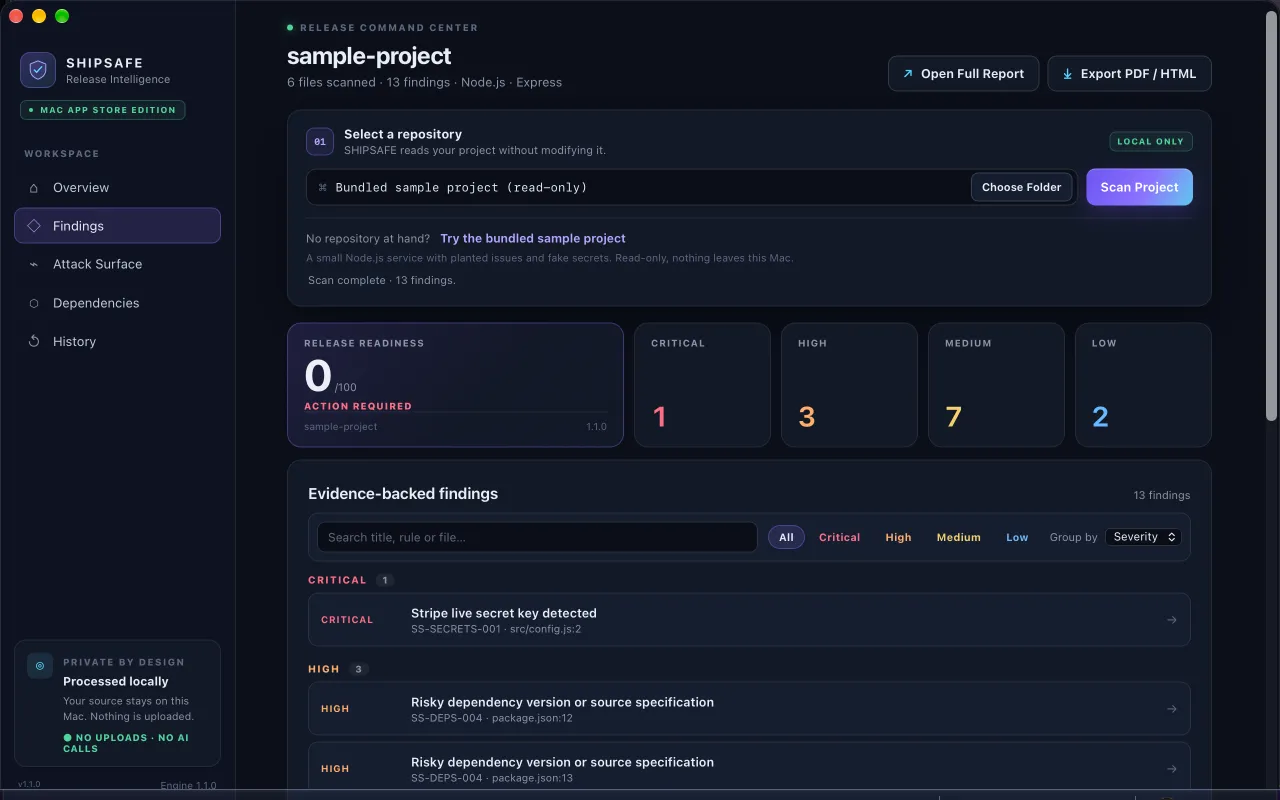
Release risks, with evidence.
SHIPSAFE reads the files of a project folder and reports what could hurt you after launch. Each finding comes with a file, a line and a suggested fix.
Leaked keys and secrets
Provider API keys, hard-coded passwords, private keys and committed .env files.
Risky release settings
Debug settings left on, sensitive routes without an evident auth guard and risky dependency versions.
Reports for your team
A release-readiness report you can share, with the evidence behind every finding.
Everything runs on your Mac.
- No upload of your code and no account
- Reads current files, not your git history
- A review assistant, not a guarantee of security
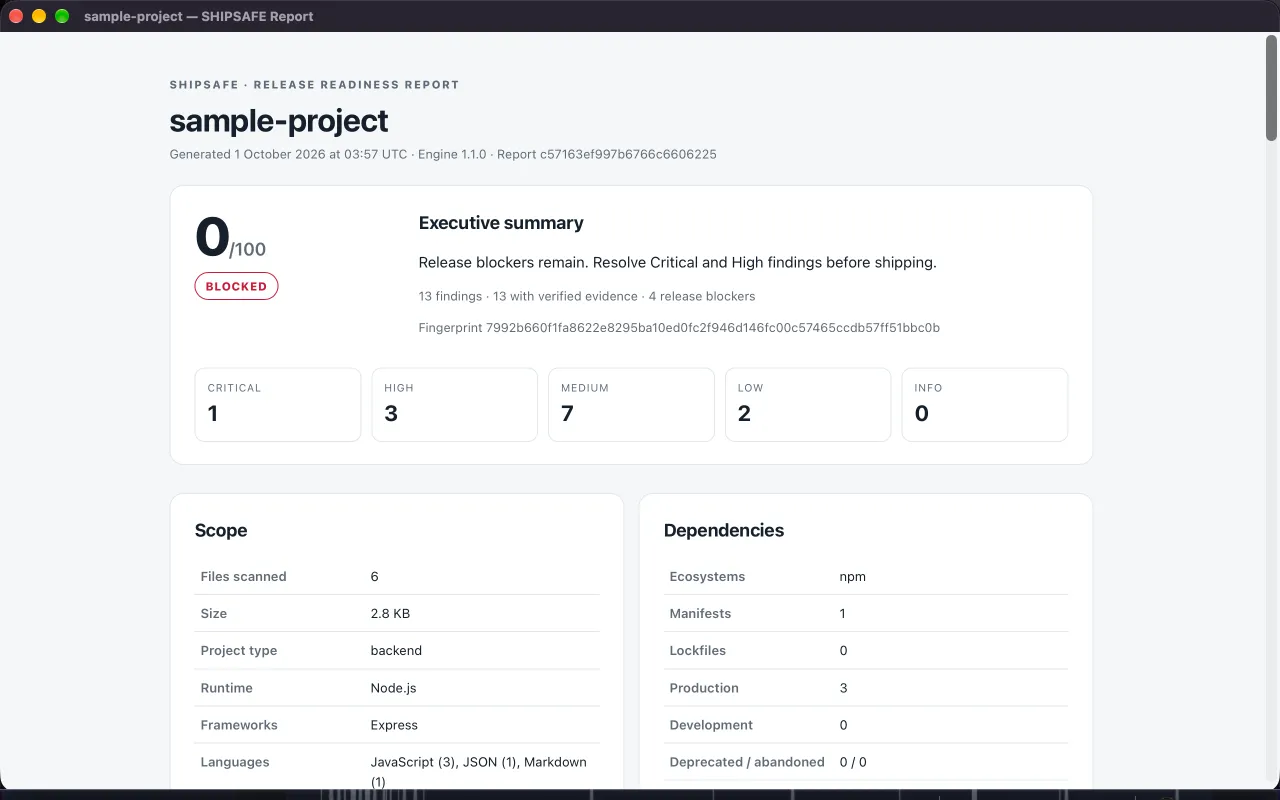
Calm, step-by-step help.
Leaked a key? Start here. Our guides are checked against the vendors’ official documentation.